Every finding links to its evidence.
No claim without a link a person can click to verify.
Security Operations Engineer building AI systems and agents that triage, review, and report, with every finding backed by evidence receipts and a human review.
I run DLP incident response and build AI agents that review 6,000+ emails and attachments a day, and show their work.
I build AI agents that securely connect log and data sources for automated reviews with severity context, and I prove they work with a measurement strategy: catch rate against a noise ceiling, evals, and human-in-the-loop review.
Incident commander for daily DLP response at Beyond Finance. I build the escalation frameworks, AI pipelines, playbooks and the fleet-wide initiatives, and I work alongside HR, Legal and exec leadership.
Critical-infrastructure security at Exelon: deployed Splunk, CyberArk, Carbon Black and Aruba ClearPass to 1,500+ RHEL and Windows Server endpoints, and owned the on-prem servers behind Splunk and CyberArk, under NERC CIP and NIST.
Follow one day of email through the review crew: a code pass, an orchestrator, six specialist reviewers, and a tuning loop that can't change its own rules.
Synthetic run · invented data50,214 emails sent outside the company today. Every one of them gets read.
Plain code parses, filters and redacts first. Duplicates, automated mail, internal business traffic and excluded teams drop out, so the model only sees what it needs.
Each packet goes to the reviewer that owns its kind of risk: customer data, financial, credentials, HR data, free-mail and quarantined mail.
All six run in parallel and log every step as it happens, so a stalled or wrong run is visible right away. Every agent reads the same context and severity playbooks from the orchestrator agent at runtime, that way severity calls stay consistent across reviewers.
Every finding links to its evidence, and an analyst confirms before anything goes out. About 15 minutes, down from roughly 5 hours of daily manual review.
A tuning agent learns from analyst decisions and call transcripts, then automatically drafts playbook changes. Nothing goes live until an engineer approves it.
No claim without a link a person can click to verify.
Tuning changes go through human review before they go live.
Parsing, filtering and redaction run as plain code, so the model only sees what it needs.
Agents read through scoped connectors, and secrets never sit in a prompt.
Every step is logged as it happens, so a stalled or wrong run is visible right away.
Every agent reads the same playbook at runtime, never answering from memory.
A single run fans out to reviewers that each own one kind of risk.
Agent changes go through branches, PRs and review, never straight to main.
Demo data is synthetic. Every email, name, count and finding above is invented, and the design is generalized from a production system. The scale is real: 6,000+ emails a day, reviewed in about 15 minutes.
Specialized agents sort outbound mail (personal, free-mail, bounced, quarantined) and add severity context. 500 → 6,000+ a day.
LiveDrafts the whole DLP incident report. 300+ written, 60–90 minutes down to under 10.
DeployedA crew of review agents, one per risk group. Each one triages open alerts, then sweeps the activity that never set one off.
LiveA multi-layer offboarding system. Every device is locked down, zero company data access after termination.
LiveGive it a name and a time window. It checks every signal source, reviews emails, and hands back a risk report with a receipt behind every claim.
Automated + on demandMeasure AI review success using catch rate to noise level thresholds from metric outputs written to a shared runlog.
Live“The agent reads every alert. The analyst reads the ones that matter.”
Away from the keyboard I'm out walking my dog, headbanging at music festivals, deep in a YouTube documentary, or using FB Marketplace as social media. Then I end up right back at the keyboard, gaming.
I'm a car guy, Acura ride or die. Keeping them spotless turned into my own detailing company, @dondetails, now six years running.
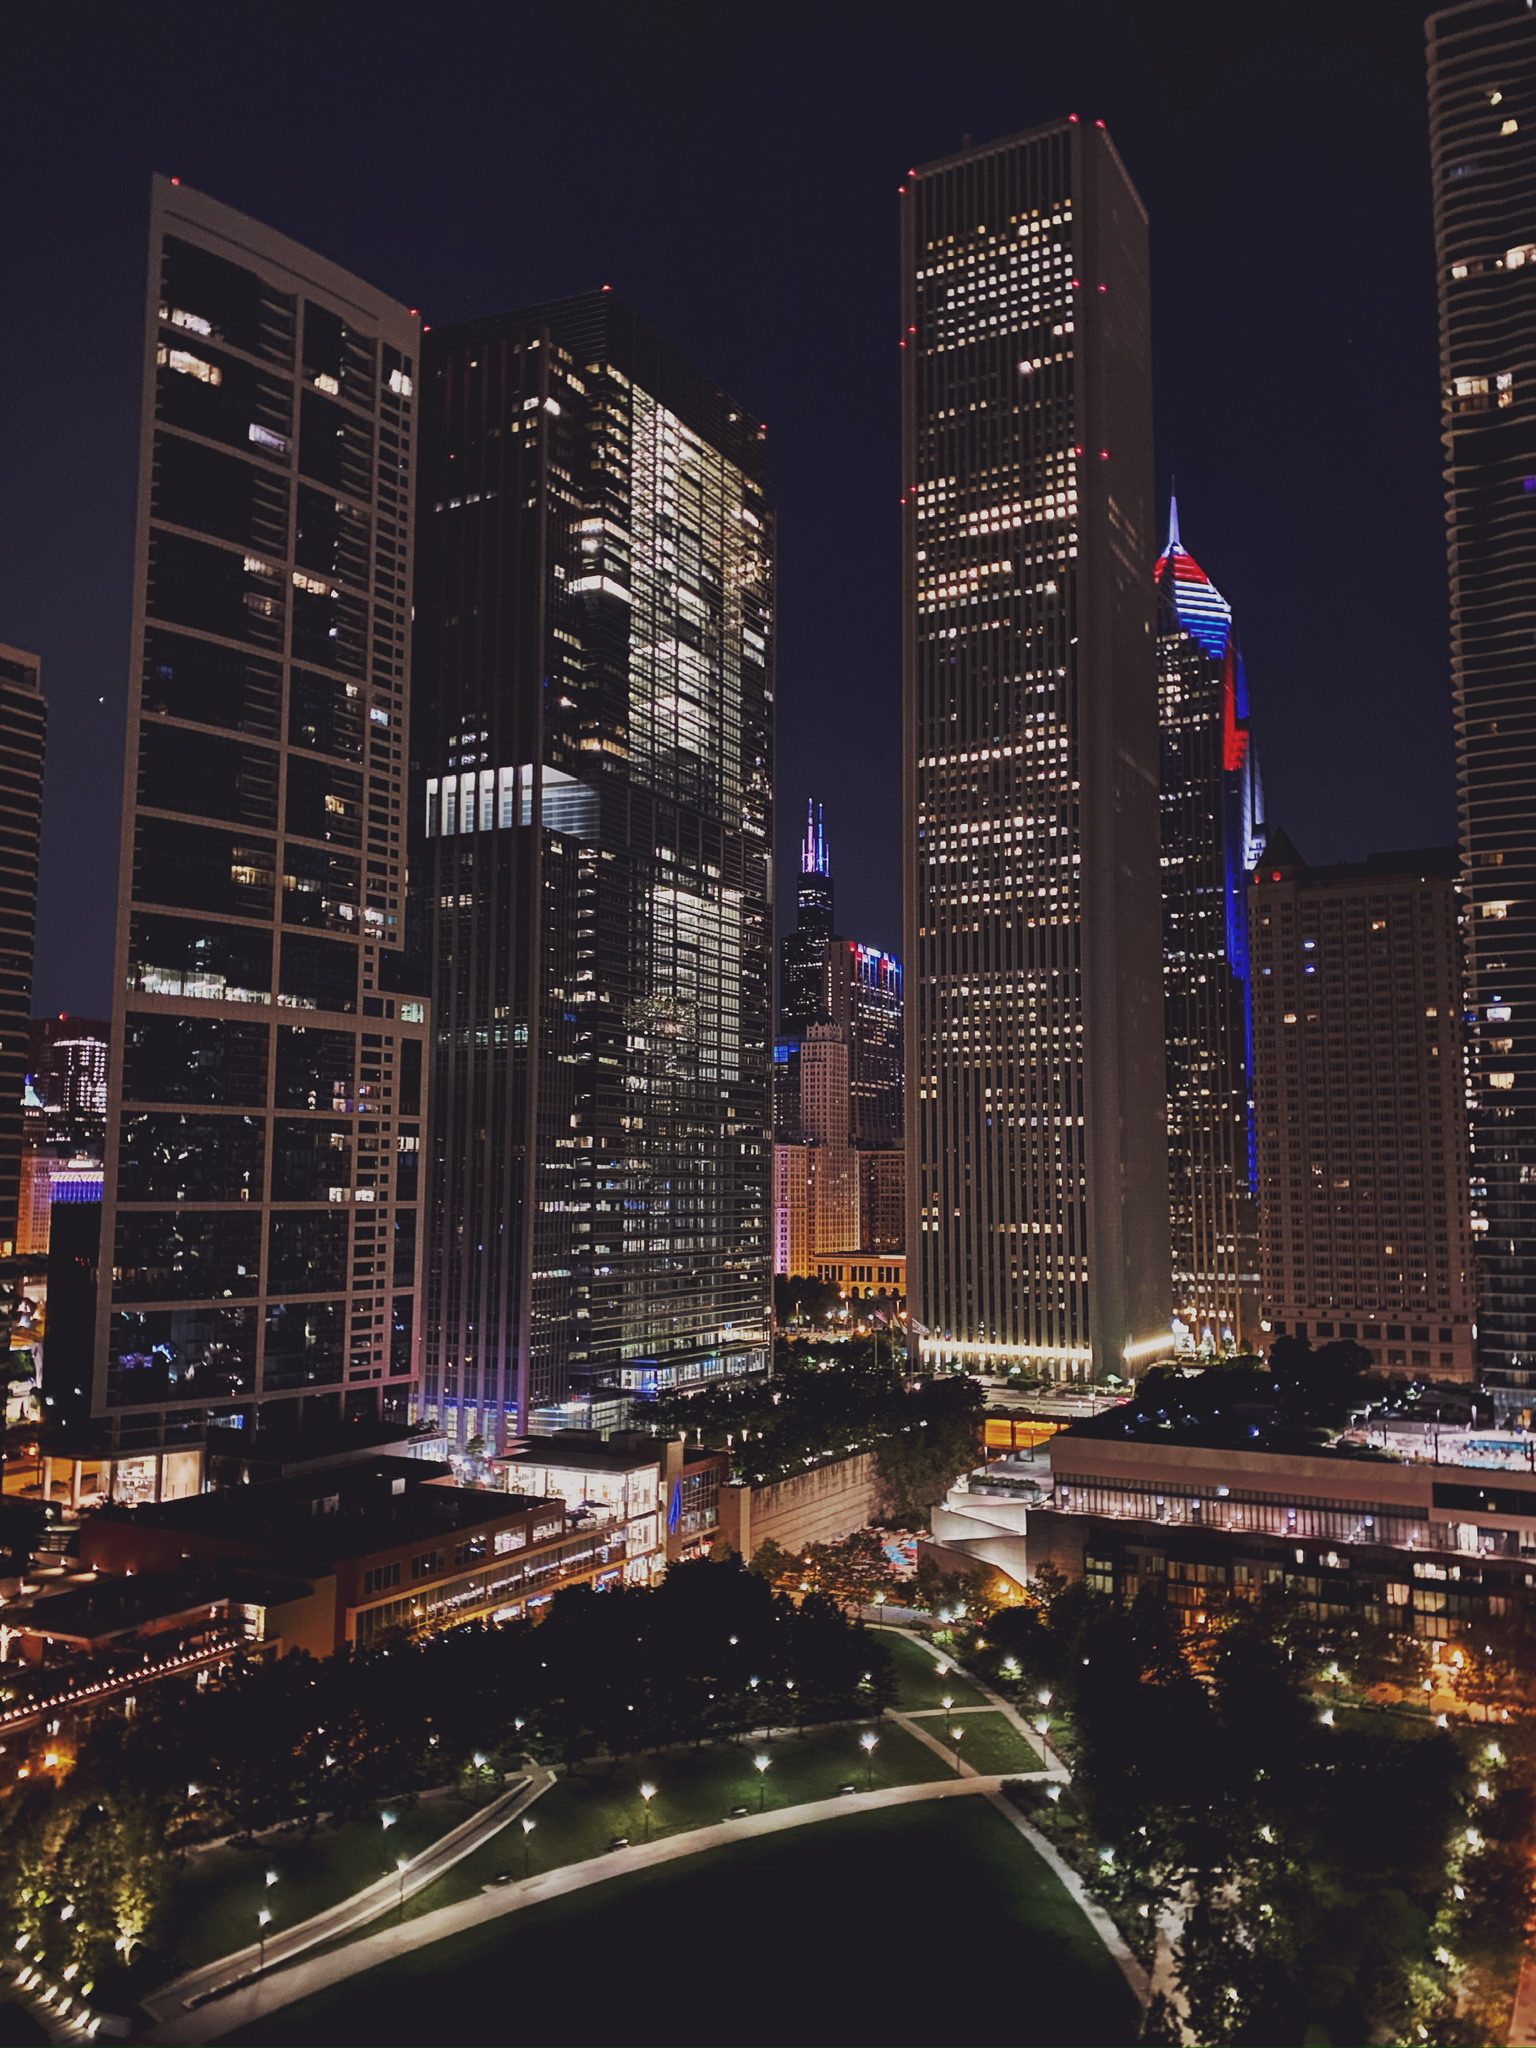
I live in Chicago's West Loop and I'm always trying new restaurants. Send me your recs, but let me put you on first: Rootstock in Humboldt Park has the best burger in the city.
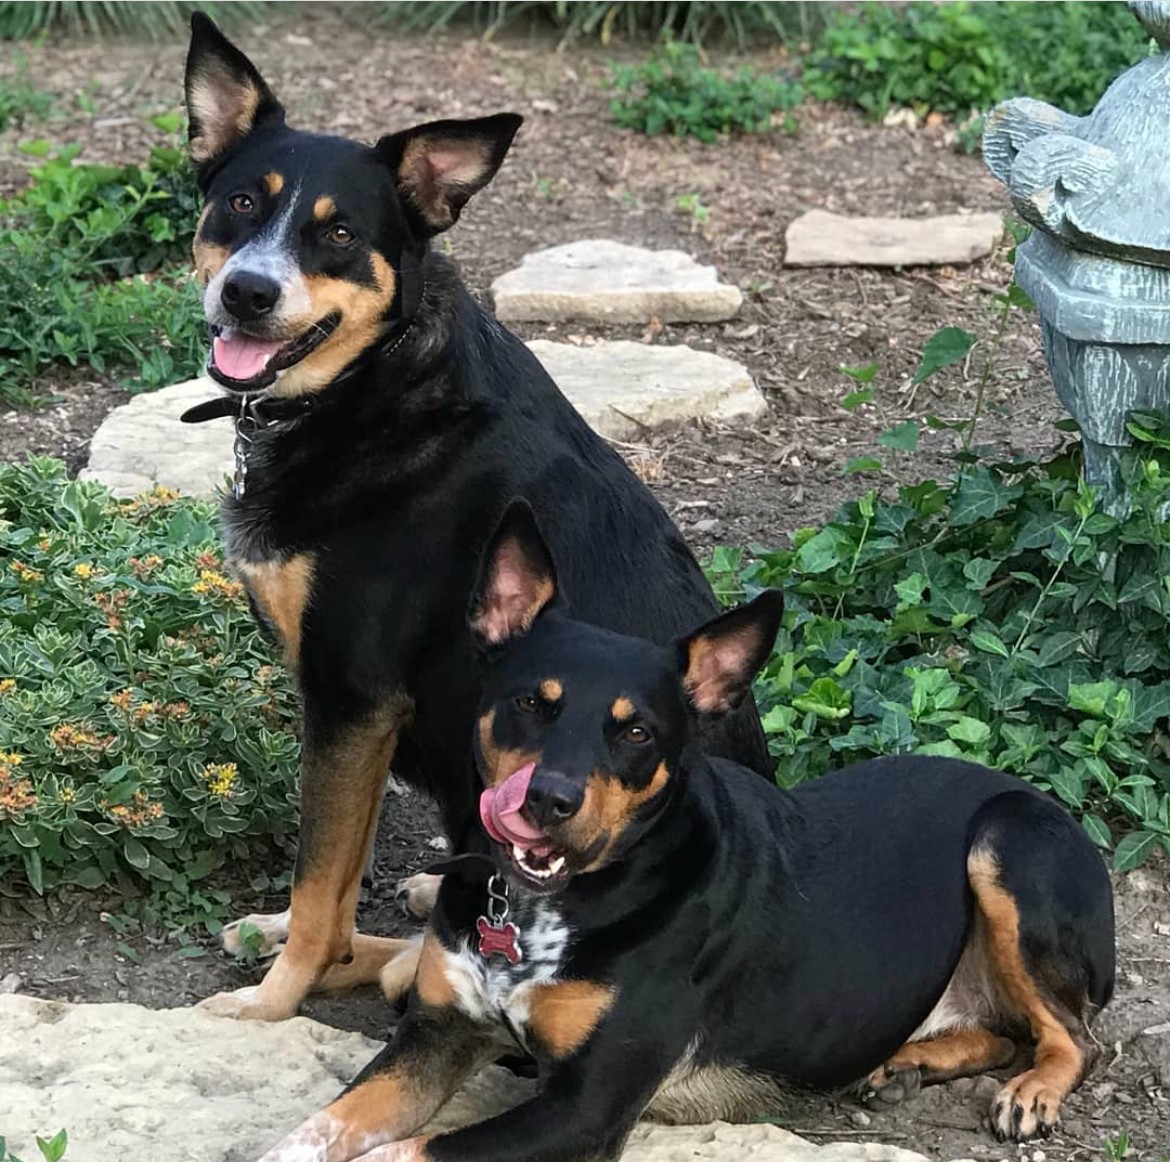 trail crew
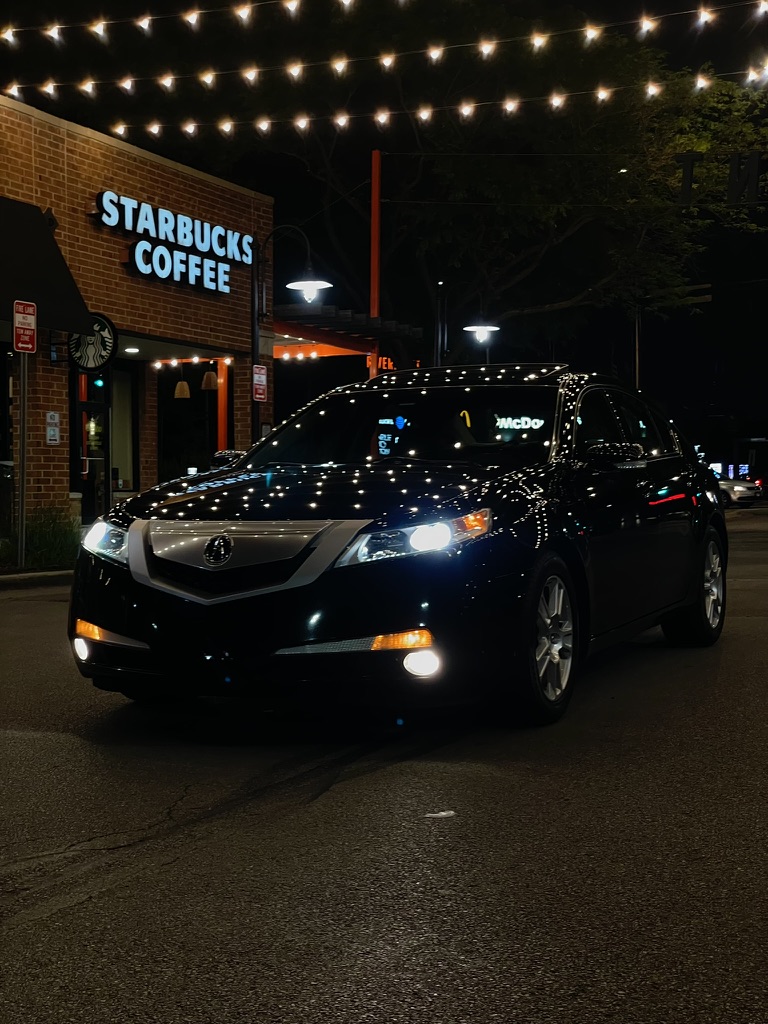 late cruise
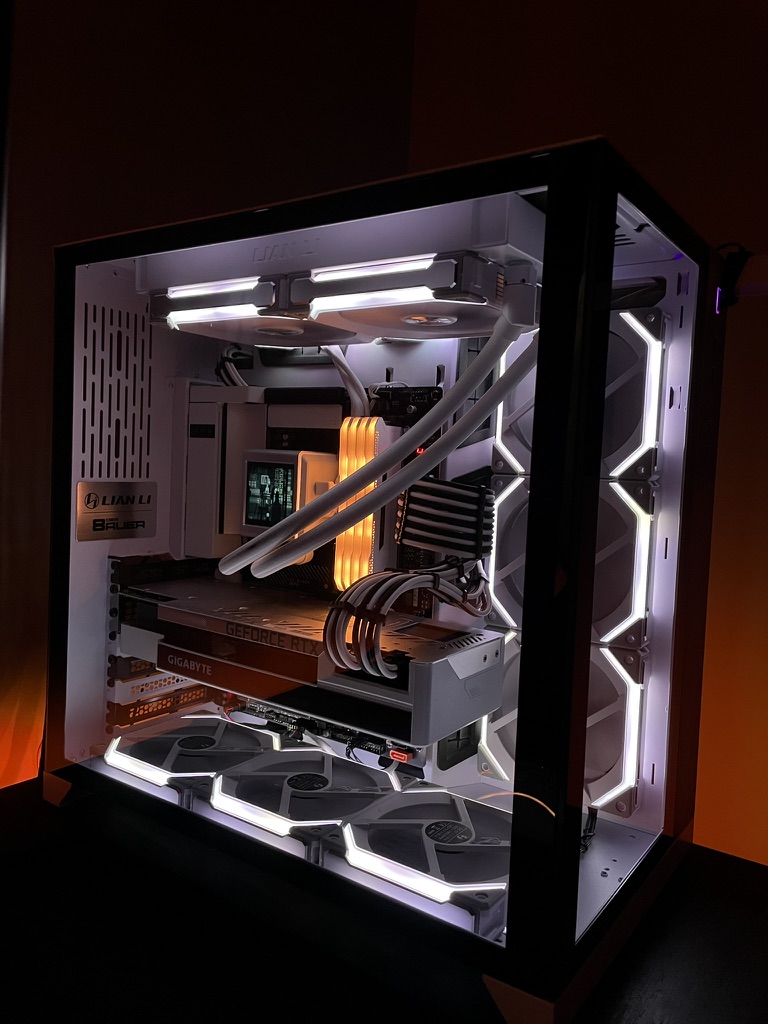 latest build
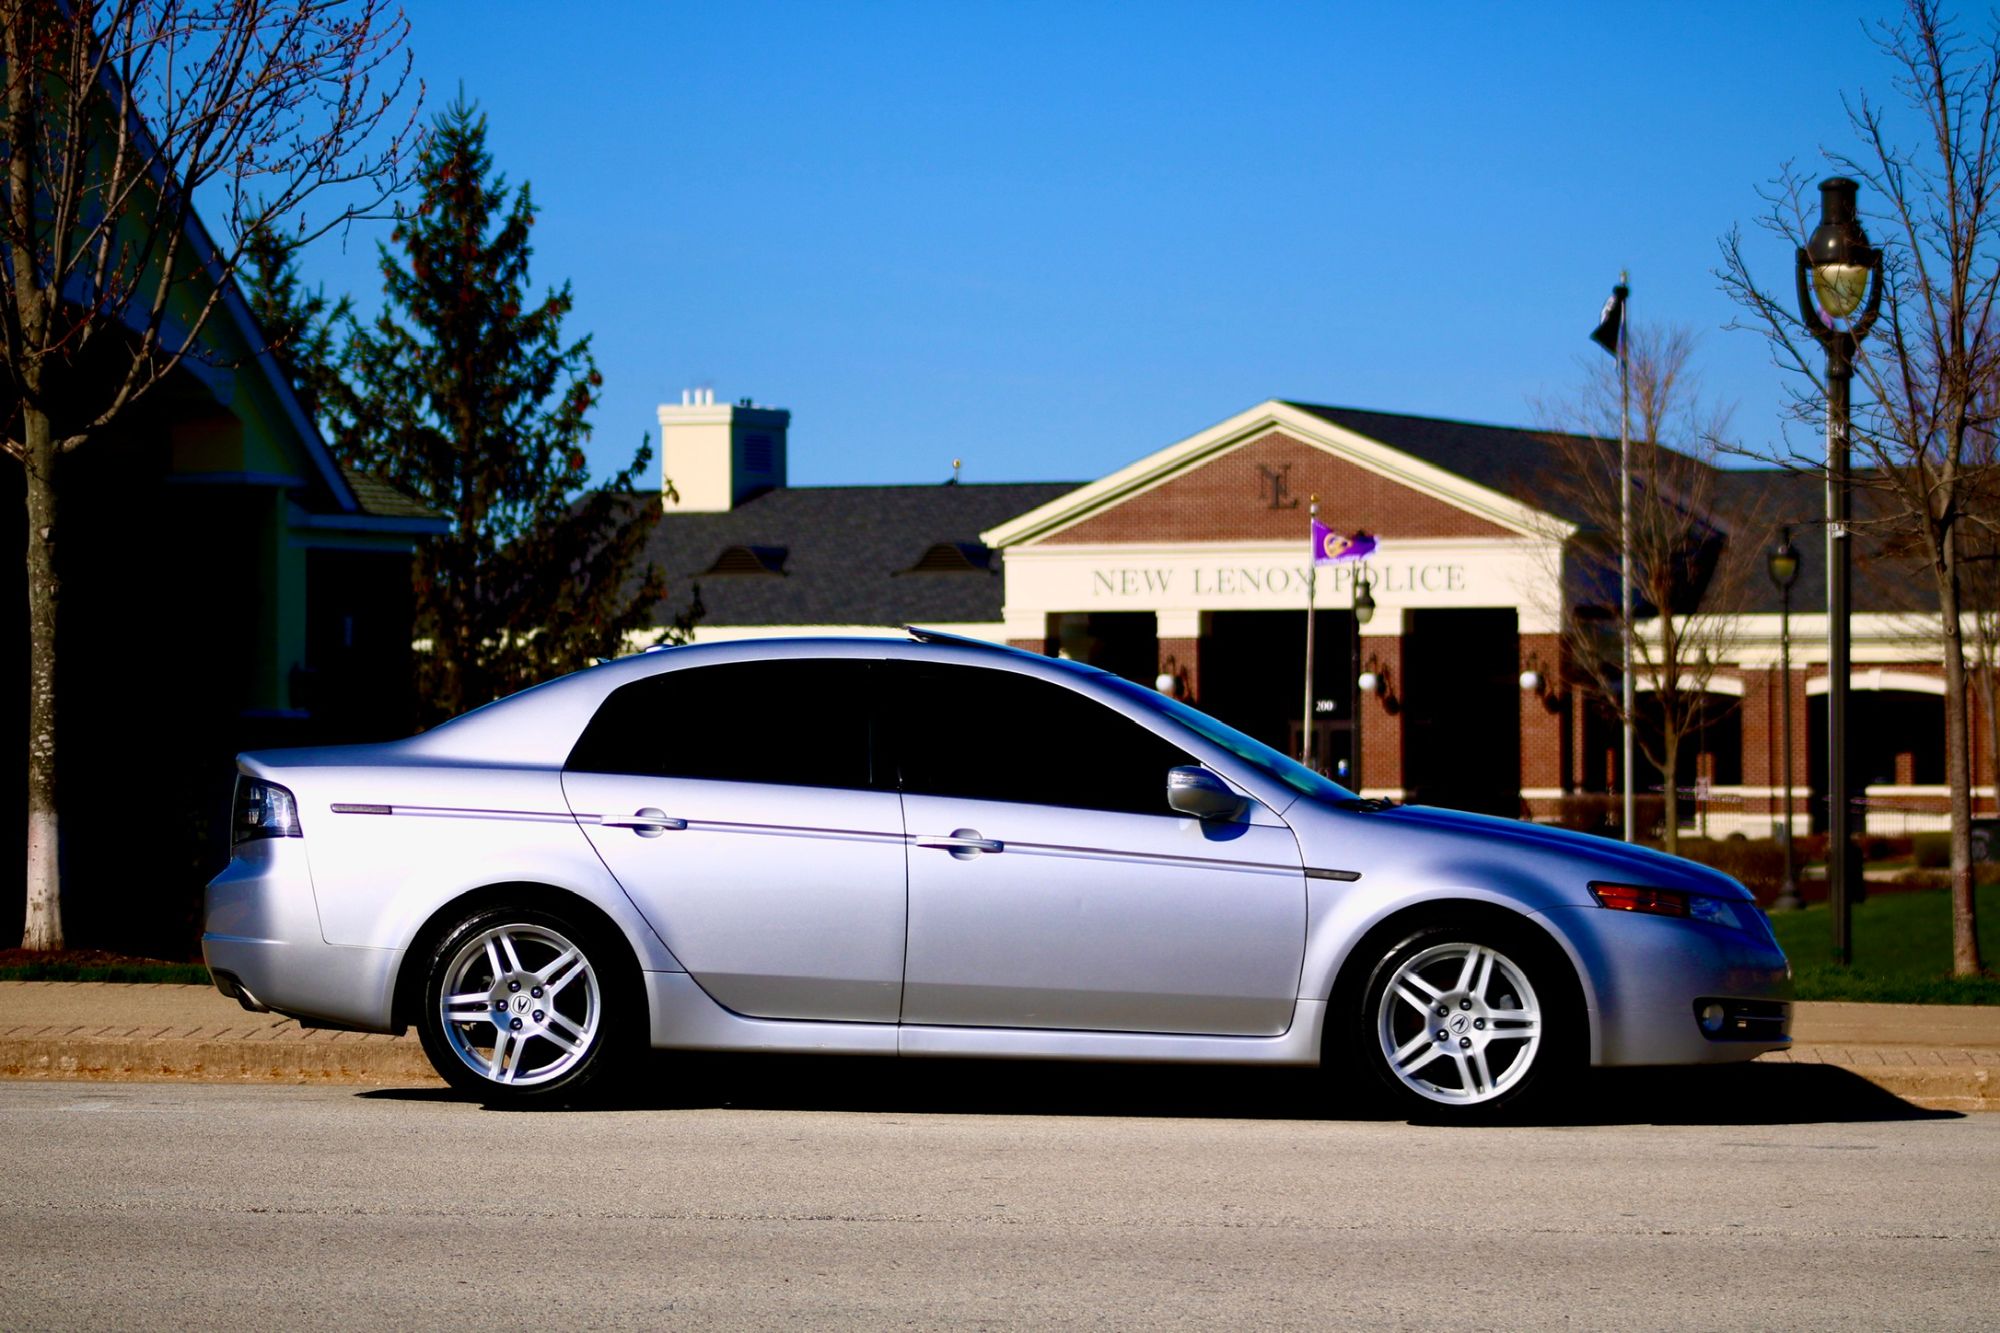 detail day
Always open to a chat about AI security, agents, or whatever you're building.